LiteLLM’s incident connects credentials to release authority
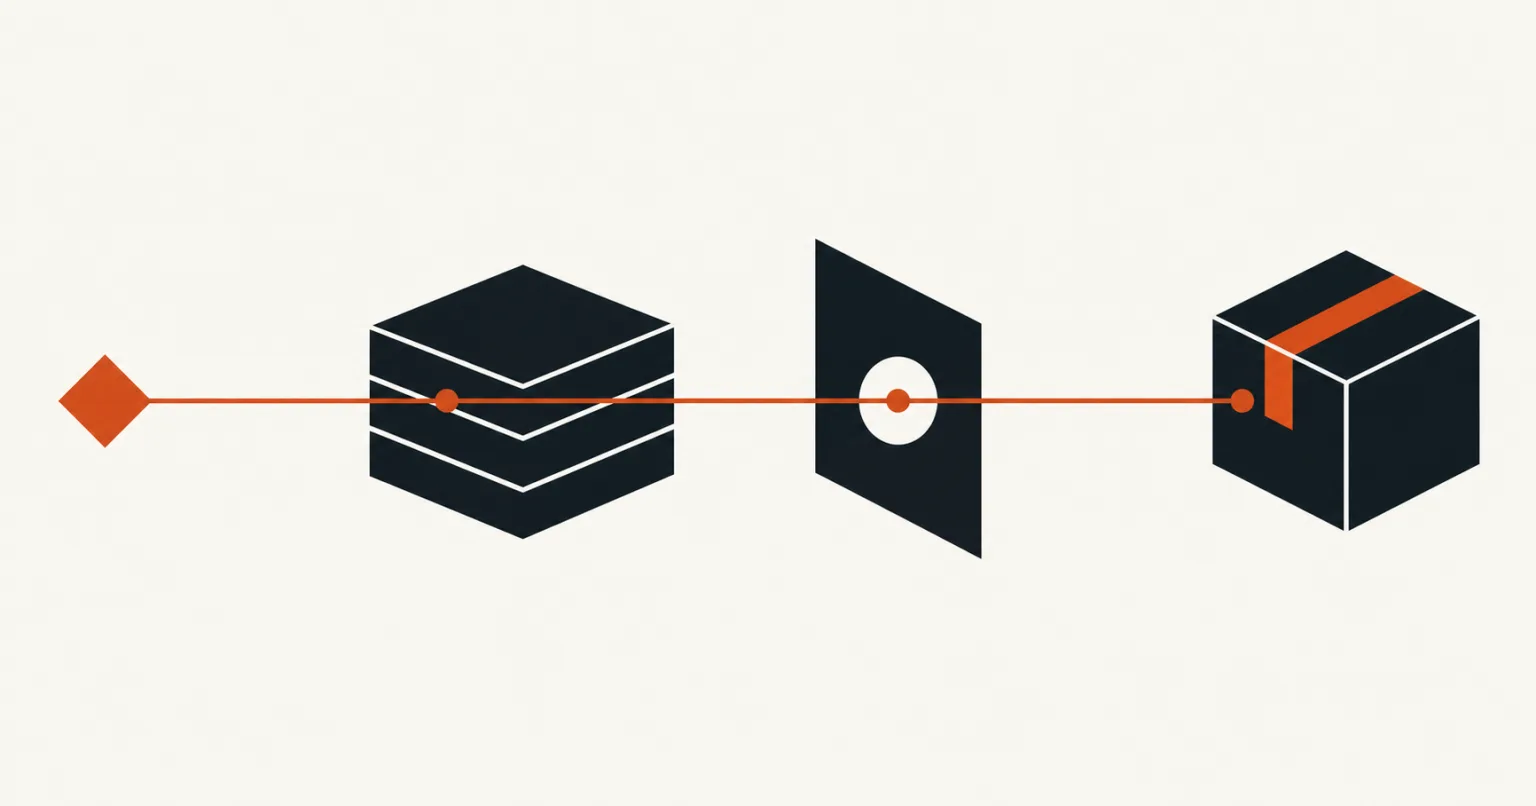
LiteLLM’s root-cause report describes a chain from exposed credentials to a malicious release. The operating question is whether apparently separate release controls depend on the same compromised authority.
As a leader: Map who can read release credentials, alter the build source, approve publication, and override the controls between those steps.
As an individual: Review the official incident record for exposure assessment and preserve the exact artifact and version used by your application.
Read the analysis →